Documentation index: llms.txt. This page is also available as markdown: append .md to this URL or send Accept: text/markdown.
Manage Users
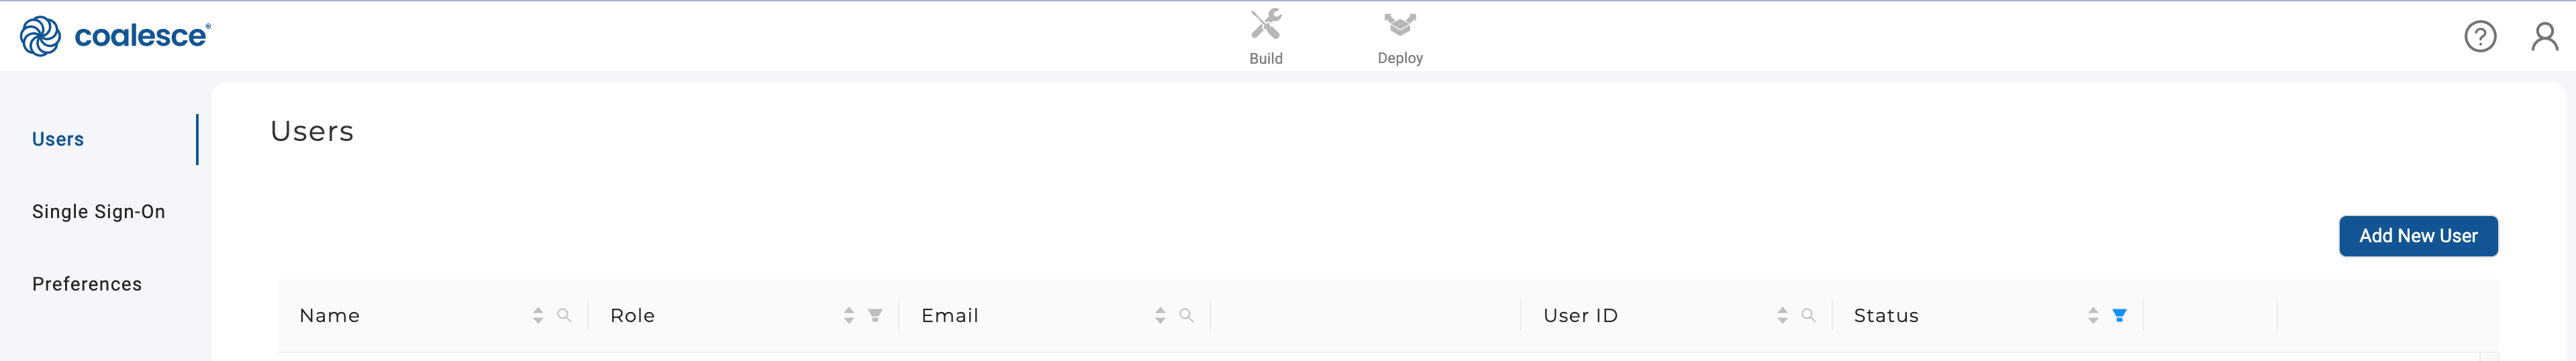
Organizations have the ability to manage users and their roles by going to User Menu >Org Settings > Users.
Add a New User
To add a new user to your organization, click the Add New User button.
In the Create User pop-up, enter the new user's account information and select Submit.
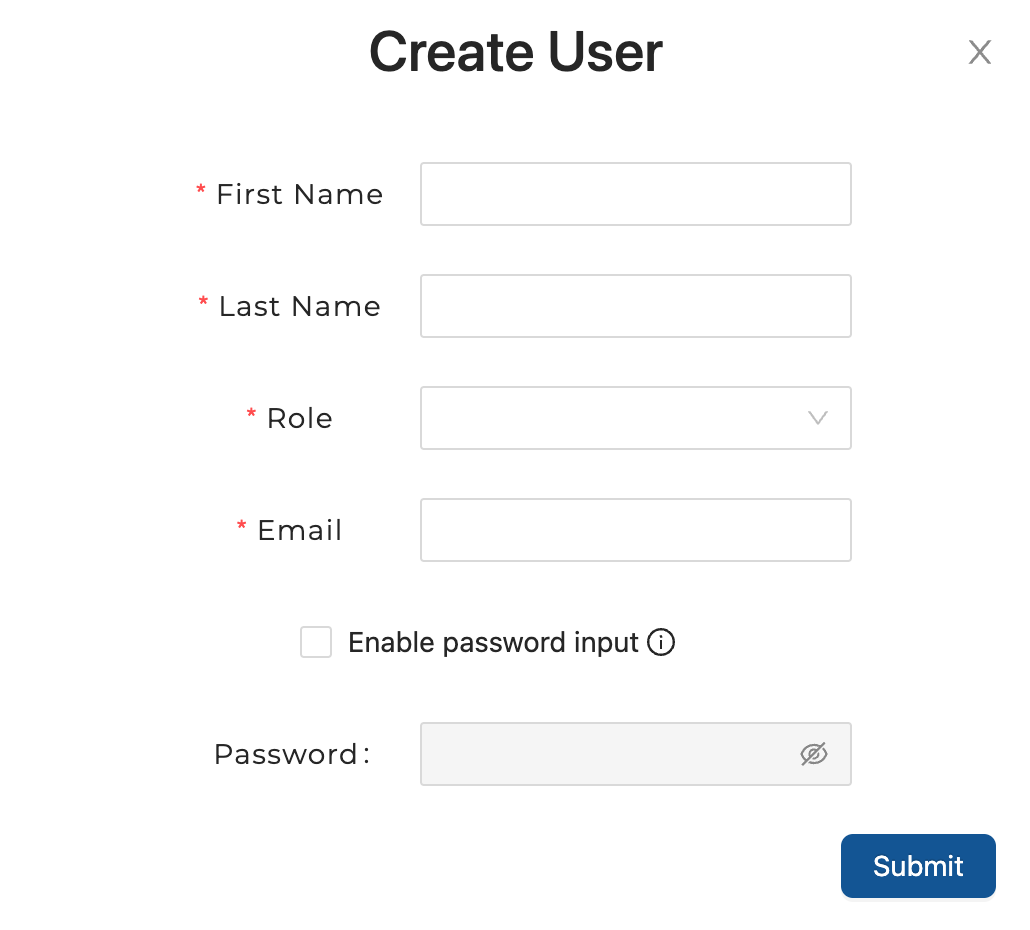
| Field | Description |
|---|---|
| First Name | User's preferred first name. |
| Last Name | User's preferred last name (hyphens are accepted). |
| Enable Password Input | If unchecked, an email will be sent to the user so they can set their password. |
| Password | If Enable Password Input is checked, the user's password will need to be manually entered in this field. |
| Role | There are two options for role designation: Admin: Has access to Org Settings such as Single Sign-On Settings and management of Users User: Does not have access to Org Settings |
Edit User
An Admin User has the option to modify a user's first and/or last name as well as the user's designated role (User vs Admin).
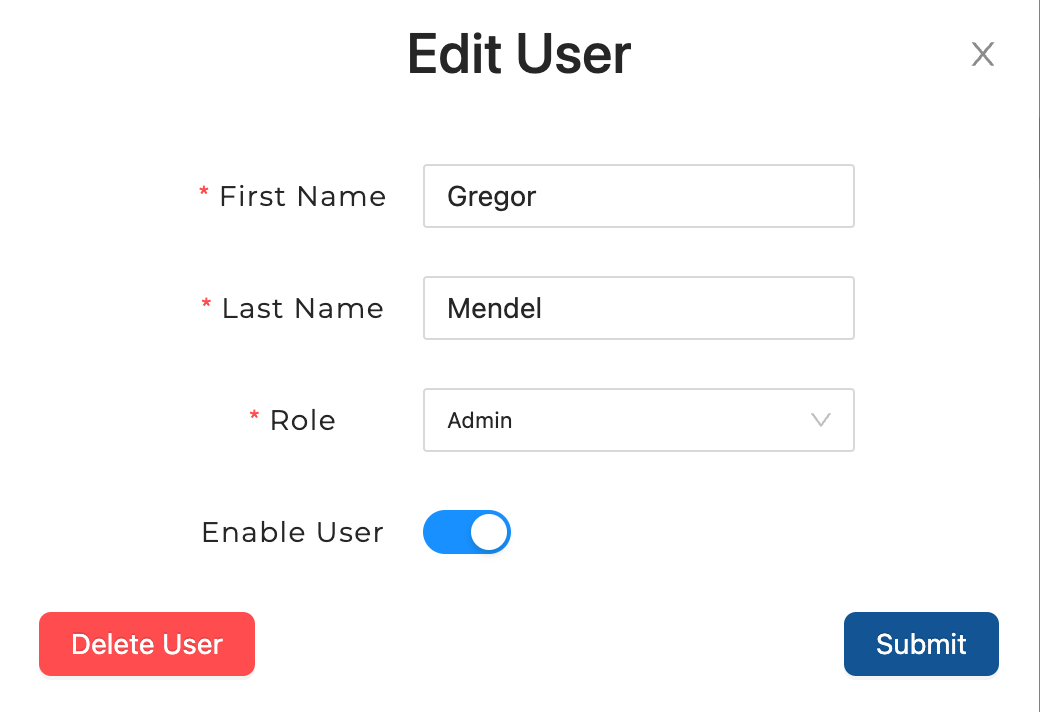
Disabling, Activating, and Deleting Users
Users can be deleted, disabled, or activated from the Edit User screen. Depending on whether your organization has moved to the Authentication Upgrade, you'll see Delete or Remove from Org.
- Deleting a user permanently removes all personally identifiable information (PII), including any user secrets. This action is irreversible.
- Removing a user with Remove from Org takes away their access to your organization only. Their account and access tokens stay in place, so they keep access to any other Coalesce organizations they belong to. This option appears for organizations on the Authentication Upgrade.
- Disabling a user will prevent them from logging in, and will log them out shortly if they happen to be logged in at the time. They can be re-enabled or activated at any time. After you re-enable a user, recover their Job Schedules with the steps in Recover a Paused Job Schedule.
Deleting, disabling, or removing a user stops every Job Schedule they last saved in your organization. Deleting or disabling also revokes their access tokens, while removing takes away their role in your organization. To get those Job Schedules running again, follow the steps in Recover a Paused Job Schedule.
Removing SSO Users
- Single Sign-On users with a username and password: Users that have been configured directly in Coalesce will be able to log in with a username and password even if SSO has been enabled or removed, as long as their Coalesce-native user record remains active. If you do not wish to allow username and password-based authentication, you must disable or delete these users.
- Users may still appear in your SSO provider's user list, but they will not be able to log in. These users must be removed manually. We recommend reviewing all deleted users to ensure they have been removed from the SSO provider.
- Access tokens function independently of SSO. Disabling a user in your SSO platform does not remove access tokens. To revoke them, delete the user directly in Coalesce. Disabling the user in Coalesce also revokes them. Removing a user from your organization doesn't revoke their tokens.
- Access tokens never expire across all environments and projects.
- Access tokens are regenerated after each login. Previously issued tokens remain valid.
For the full list of actions that revoke access tokens, which depends on whether your organization has moved to the Authentication Upgrade, see Access Token Revoked.
When To Contact Support
Org admins can add users, change roles, and manage access directly in the Coalesce App. Some account and access requests are handled by the Coalesce team and are not self-service.
Self-service (org admins):
- Add users to your organization.
- Edit user names and roles (Admin vs User).
- Disable, activate, or delete users.
- Assign RBAC roles at the organization, project, and environment levels.
Support-assisted (contact Coalesce):
- New Catalog accounts for new customers.
- New customer organization setup.
- POC account setup and adding specific users.
When requesting new accounts or access, include the following in your support request:
- Customer or organization name.
- Key user email addresses.
- Integrations needed (for example, Snowflake, Sigma, Coalesce Transform).
- Timeline and any organizational context (for example, merger, hierarchy change).