Documentation index: llms.txt. This page is also available as markdown: append .md to this URL or send Accept: text/markdown.
Service Accounts in Coalesce
Service accounts are non-human accounts used to run automated processes, deployments, and scheduled jobs in Coalesce. Unlike individual user accounts, service accounts aren’t tied to a specific employee. This makes them more reliable for production workloads and easier to manage when team members change.
This guide explains how to configure service accounts, assign the correct roles, set up authentication, and follow security and licensing best practices.
Role and Permission Recommendations
Service accounts should follow the principle of least privilege. Only assign the roles needed for their intended purpose.
- Org Contributor
- Org Member
- Project Member
- Environment Reader
- Environment Admin (only if the service account must deploy, refresh, or own Job Schedules)
If a service account is responsible for deployments, refreshes, or Job Schedules, it must have the Environment Admin role.
Authentication Method
For service accounts, key pair authentication is strongly recommended. Key pairs provide stable machine-to-machine connections, reduce overhead, and avoid issues with expiring tokens. OAuth or username/password authentication should be avoided when setting up service accounts.
Use Cases and Best Practices
Service accounts are best suited for tasks where human intervention isn’t required:
- Production deployments and refreshes: Keeps these processes separate from personal accounts.
- Scheduled jobs and automated processes: Ensures jobs continue running even if team members leave. See Run Job Schedules as a Service Account.
- CI/CD processes: Allows external tools to automate deployments securely.
Environment Strategy
Use personal accounts for development work. Reserve service accounts for higher environments such as QA, UAT, and Production.
For stronger security isolation, consider creating separate service accounts for each environment.
Licensing and Management
- Service accounts do not count toward your Coalesce license allocation.
- Most organizations use one or two service accounts.
Security Considerations
To keep service accounts secure, follow these best practices:
- Use distribution list emails instead of personal email addresses.
- Distribute private keys securely using encrypted methods.
- Assign only the minimum required privileges for the account’s role.
- Don't share access tokens in plain text, for example in chat or email. If a token is exposed, an Org Admin can revoke it with the token revocation endpoint. Revoking stops every Job Schedule the service account last saved, so sign in as the service account and follow Recover a Paused Job Schedule for each one.
Steps to Create a Service Account in Coalesce
Follow these steps to create and configure a service account in Coalesce:
-
Go to the top right of the Coalesce interface and click Organization Settings.
-
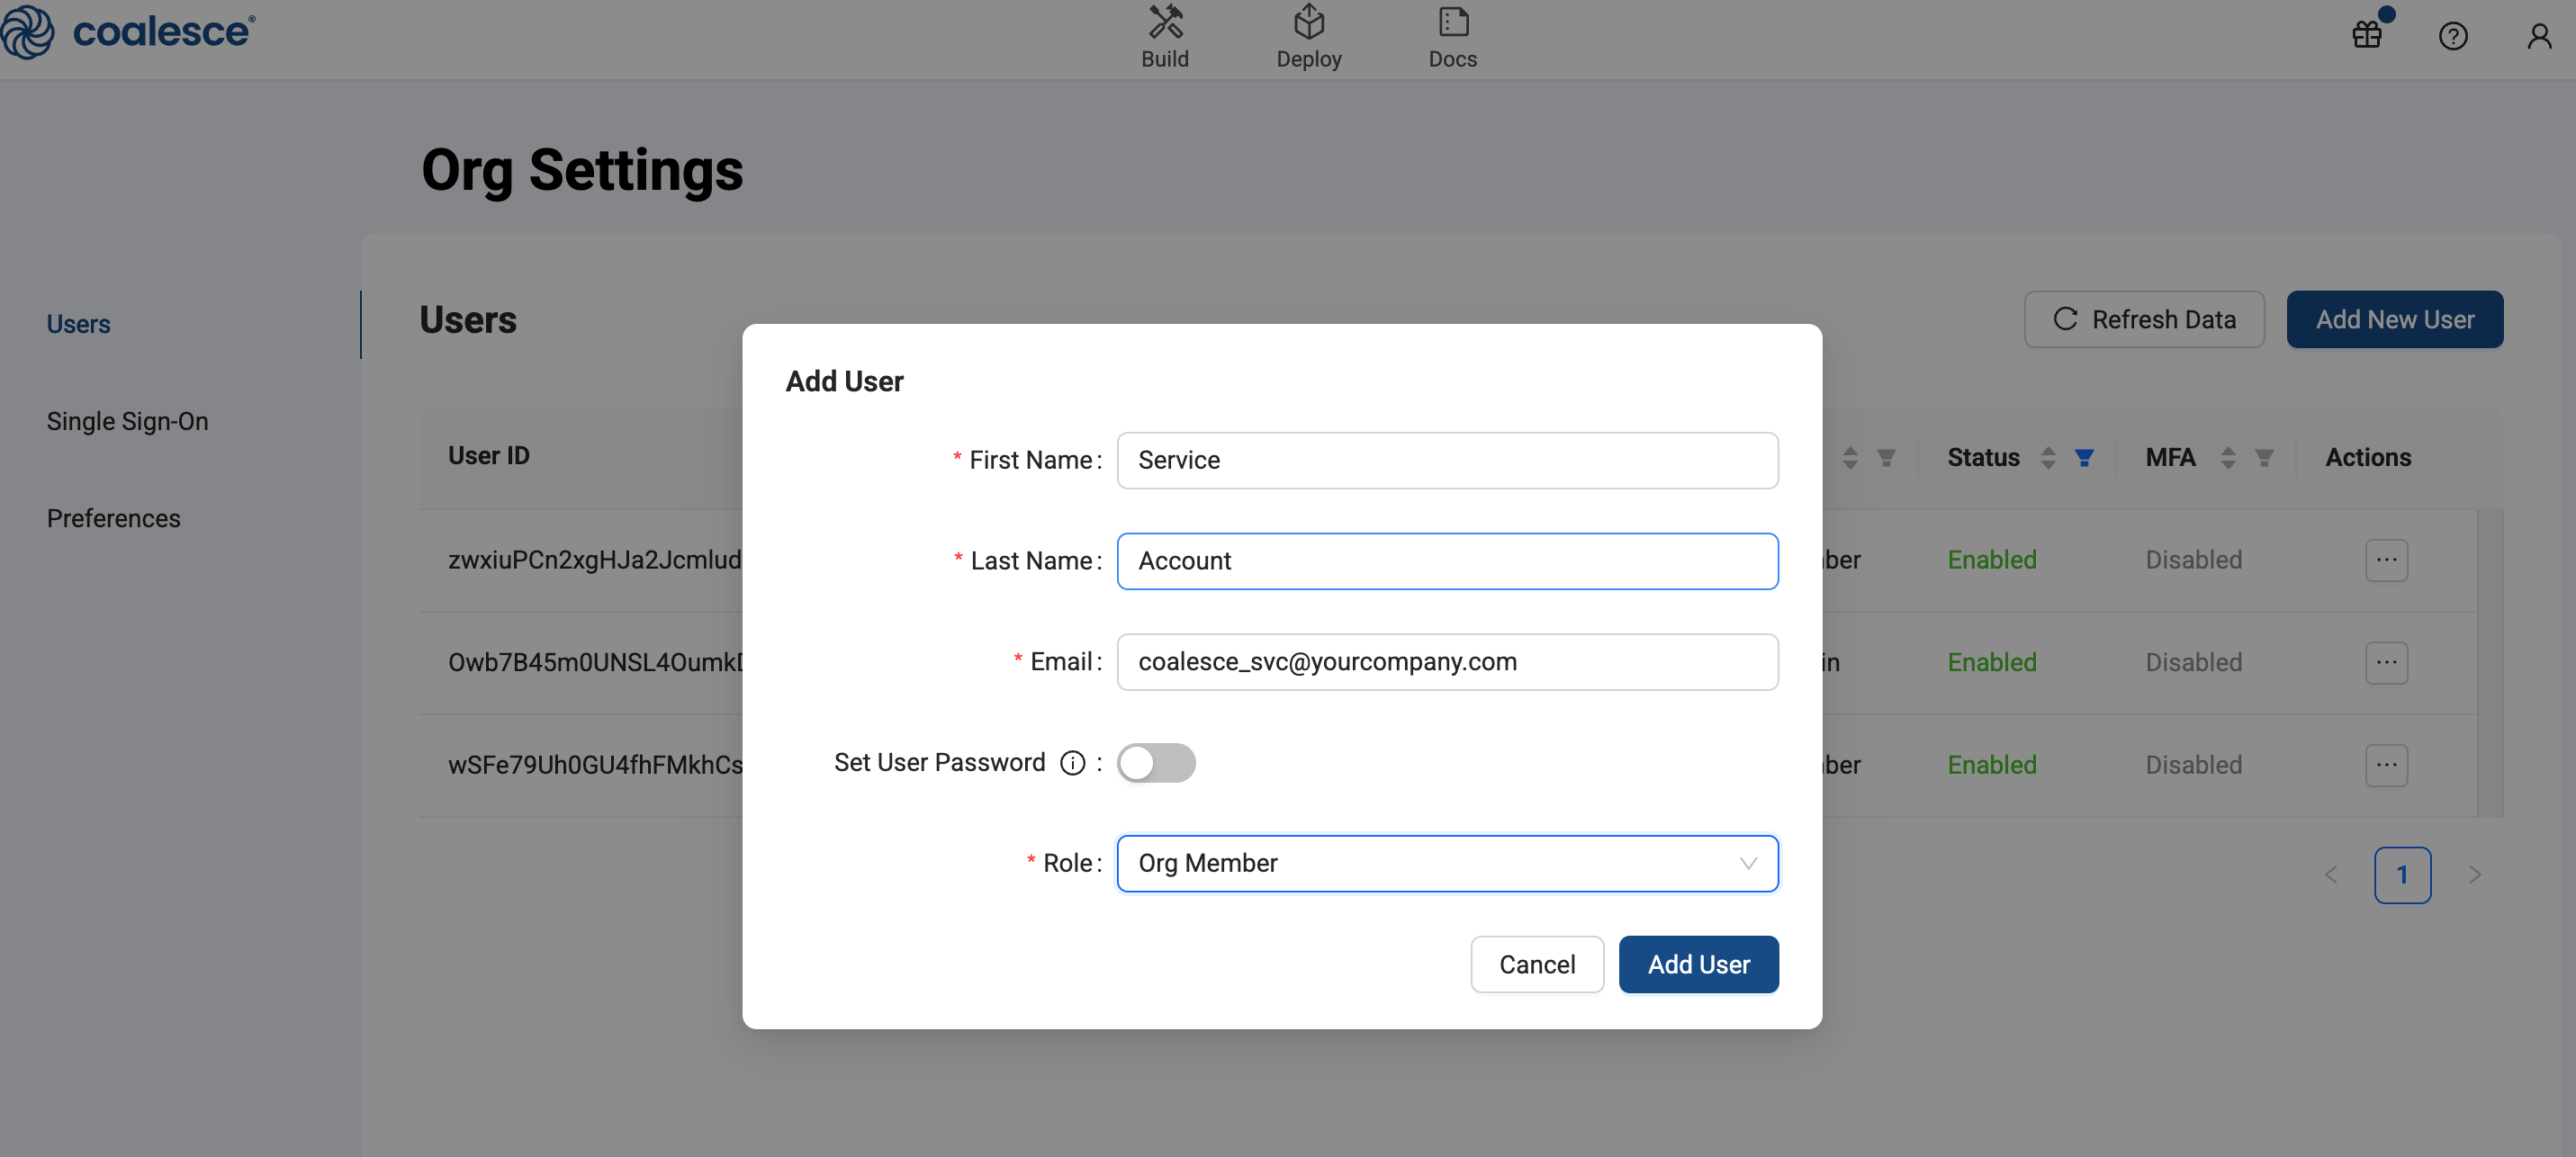
Click Add New User.
- Set the first name as Service and last name as Account (or use a similar naming convention).
- Use a distribution email address such as
coalesce_svc@yourcompany.cominstead of a personal email.
-
Assign the service account to the appropriate role based on its intended use. You'll need to set it on the Org, Project, and Environment level. If the service account is used for deployments, ensure it has the necessary environment permissions.
-
Choose your authentication method. We recommend:
- Key Pair for Snowflake
- Machine-to-Machine for Databricks
-
If your Coalesce project integrates with Snowflake, create a corresponding service account in Snowflake using SQL:
   USE ROLE USERADMIN;
   CREATE USER <SERVICE-USER-USERNAME> PASSWORD='<SERVICE-USER-PASSWORD>'
   FIRST_NAME='DCR' LAST_NAME='Service User'
   EMAIL='<SERVICE-USER-EMAIL-ADDRESS>';
Run Job Schedules as a Service Account
Each Job Schedule runs as the user who last saved it, with that user's access token and data platform credentials. To run a Job Schedule as the service account, save it while you're signed in as the service account.
- Sign in to Coalesce as the service account.
- In each Environment where the service account runs Job Schedules, add the service account's data platform credentials. Runs use only the credentials of the user the Job Schedule runs as, so credentials that other users saved don't apply.
- Create the Job Schedule, or open an existing one from the Jobs Schedule page and select Edit, then Save. If the Job Schedule is paused, select Resume.
For more on how Job Schedules use credentials, see Scheduling Jobs in Coalesce.
Who Can Change a Service Account's Job Schedules
Any Org Admin, Project Admin for the Job Schedule's Project, or Environment Admin for its Environment can edit, pause, resume, or delete the Job Schedule. Saving it makes the Job Schedule run as the person who saved it, with their credentials. Pausing, resuming, or deleting it doesn't change who it runs as.
Choose who should have these roles based on what you need:
- Keep Job Schedules running as the service account - Give Org Admin only to the people who manage the service account. In the Projects and Environments where the service account runs Job Schedules, limit Project Admin and Environment Admin the same way.
- Let someone else pause or resume Job Schedules - Keep at least one trusted person in one of these roles. They can pause and resume without taking over, but if they save a Job Schedule, it runs as them.
- Recover a paused Job Schedule without changing who it runs as - Sign in as the service account, then select Edit, Save, and Resume. See Recover a Paused Job Schedule.